
| tsti's 2025 Digital Trust framework
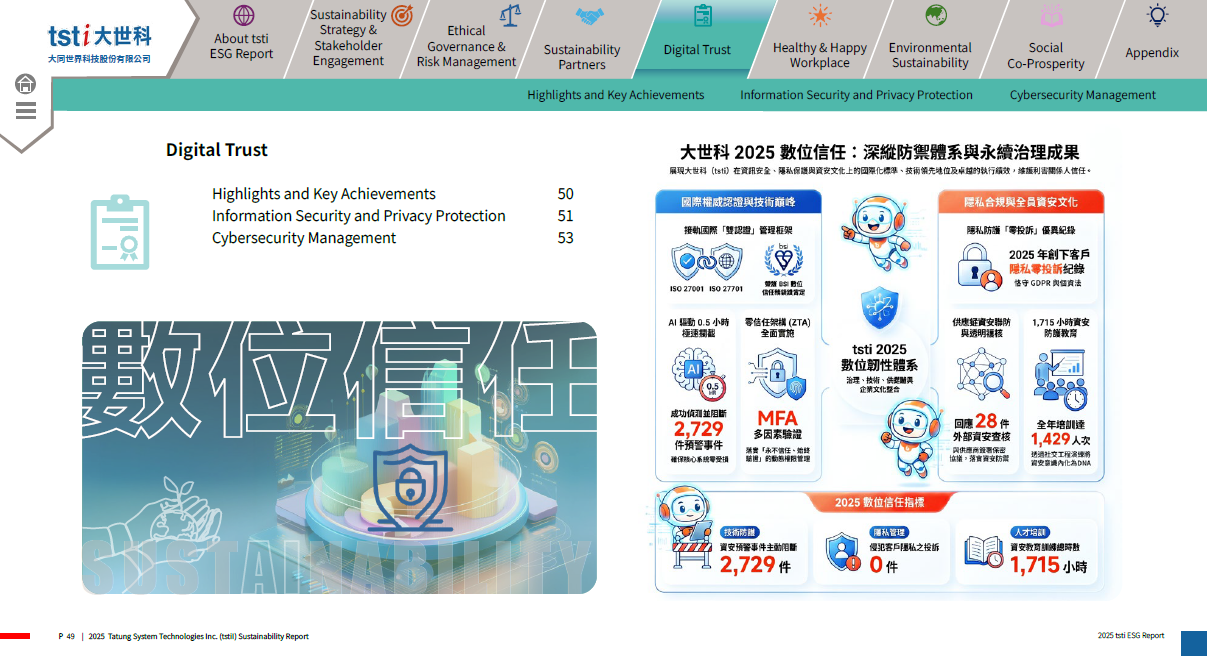
In 2025, Tatung System Technologies Inc. (tsti) built its corporate sustainability resilience and stakeholder relations upon a robust Digital Trust (數位信任) framework. Driven by an organizational security culture of "Proactive Defense and Immediate Response". the company synchronized international standards, structured management processes, and advanced AI-powered technical systems to protect its operations and customer data.
The details of tsti's 2025 Digital Trust framework, as outlined in the sources, include:
1. Robust Information Security & Privacy Governance
- Dedicated Oversight: Strategic governance is managed by the Cybersecurity and Privacy Management Task Force (which evolved from the board-level committees in late 2023 to sharpen operational execution). The task force convened 4 regular working meetings in 2025 and presented its annual cybersecurity governance report to the Board of Directors in the fourth quarter to support executive decision-making.
- Increased Cybersecurity Investments: In response to rising external threats, tsti expanded its annual cybersecurity spending to NT$ 4,152 thousand in 2025 (representing a steady increase from NT$ 3,067 thousand in 2024 and NT$ 2,290 thousand in 2023). This funding supports software/hardware warranties, consulting, security equipment, and office systems.
- Compliance Automation: To mitigate human error and ensure operational continuity, tsti implemented digital tools to automate compliance workflows for ISO 27001 (Information Security), ISO 27701 (Privacy Protection), and ISO 20000-1 (Service Management0. They also introduced automated configuration check reports in 2025 to enforce setting consistency across systems.
2. Dual International Certification & Recognition
- Continuous Dual Integration: tsti successfully passed the ISO/IEC 27001:2022 continuous audit on its first attempt and maintained its ISO/IEC 27701:2019 (Privacy Information Management System, PIMS) certification. The company has integrated both systems into a single management framework to streamline workflows and boost administrative efficiency.
- BSI Elite Award: For outstanding implementation of these international standards, the company was honored with the "Digital Trust - Elite Award" at the BSI Digital Trust International Standards Management Annual Conference.
3. Active Multi-Layered Security & Incident Management
- Zero-Trust Architecture (ZTA): tsti systematically implemented ZTA under the core tenet of "Never Trust, Always Verify," executing dynamic identity authentication, device legitimacy, and Multi-Factor Authentication (MFA) paired with the Principle of Least Privilege (PoLP).
- AI-Driven Automated Joint Defense: By combining endpoint protection (EDR/XDR), firewalls, and Security Information and Event Management (SIEM) systems, tsti built an AI-driven monitoring platform. Backed by 24/7 Security Operations Center (SOC) services, this platform successfully detected and mitigated 2,729 Tier-1 and Tier-2 early-warning events (such as malware probes and anomalous connection attempts) in 2025.
- Rapid Containment Performance: Due to these automated monitoring systems, all 2,729 security events were contained and resolved within 0.5 hours, ensuring zero operational disruption or compromised systems.
- Proactive Vulnerability & Supply Chain Control: The company conducts regular vulnerability scanning, penetration testing, and red team exercises in partnership with TWCERT/CC and threat intelligence platforms to deploy patches before exploit attempts. Additionally, it uses a standardized supplier cybersecurity rating framework to run annual desk reviews and on-site audits for critical vendors.
- Cloud Security Guardrails: tsti strengthened its cloud governance by deploying Microsoft Purview to manage sensitive data and optimizing its Azure configurations with Cloud Security Posture Management (CSPM) and Cloud Workload Protection Platforms (CWPP).
4. Personal Data Protection & Privacy Regulation Compliance
- Strict Regulatory Alignment: tsti adheres to the Personal Data Protection Act (PDPA) through its "Personal Data File Security Maintenance Plan and Post-Business Termination Personal Data Disposal Procedures". This framework is co-managed and audited by the Legal Affairs Unit and the Cyber Security Department.
- Zero Breaches & Audits: In 2025, tsti recorded zero confirmed data leak incidents and received zero complaints regarding customer privacy violations or loss of customer data.The company also successfully processed and responded to 28 cybersecurity audit and inquiry requests from external stakeholders, including government authorities and clients.
- NDA and Process Safeguards: The company utilizes technology to ensure employees comply with Non-Disclosure Agreements (NDAs) and has integrated the Power Automate platform to systematically convert manual, labor-intensive workflows into secure, automated processes.
5. Professional Talent & All-Employee Security Culture
- High-Volume Awareness & Training: To keep pace with evolving threats, starting in October 2025, tsti increased the frequency of its corporate cybersecurity campaigns from monthly to twice a month. The training statistics for 2025 reached record highs:
- Cybersecurity Awareness Campaigns: Released 22 times, accumulating 11,000 attendee-times.
- Specialized Education & Training: Attracted 1,429 attendee-times, totaling 1,715 cumulative hous.
- Targeted Training Courses: On September 23, 2025, the Head of Legal Affairs and the Head of Cyber Security co-lectured the "2025 Personal Data & Information Security Awareness Course," training over 200 employees on compliance, trends, and real-world incident case studies.
- Professional Credentials: Cybersecurity personnel actively upgraded their expert technical capabilities; the cybersecurity manager completed CISSP professional training, while other personnel completed CEH offensive and defensive technical courses.
- Action-oriented drills: The company routinely executes social engineering and phishing email simulations, integrating these drill results directly into employee performance evaluations to sustain high vigilance.
Please refer to the Sustainability Report [PDF] relevant chapter for more details.